How to Build CI/CD Pipelines Using GitHub Actions
GitHub Actions is now one of the most widely adopted CI/CD platforms, partly because it lives inside the same repository where code is written and reviewed. There is no separate server to configure, no external webhook setup, and no credential handoff between different systems. For teams already using GitHub, building CI/CD pipelines using GitHub Actions is often the fastest path to automated builds, tests, and deployments. This guide walks through how it works, how to structure effective workflows, and how to move beyond basic automation into more sophisticated pipeline patterns.
How GitHub Actions Works
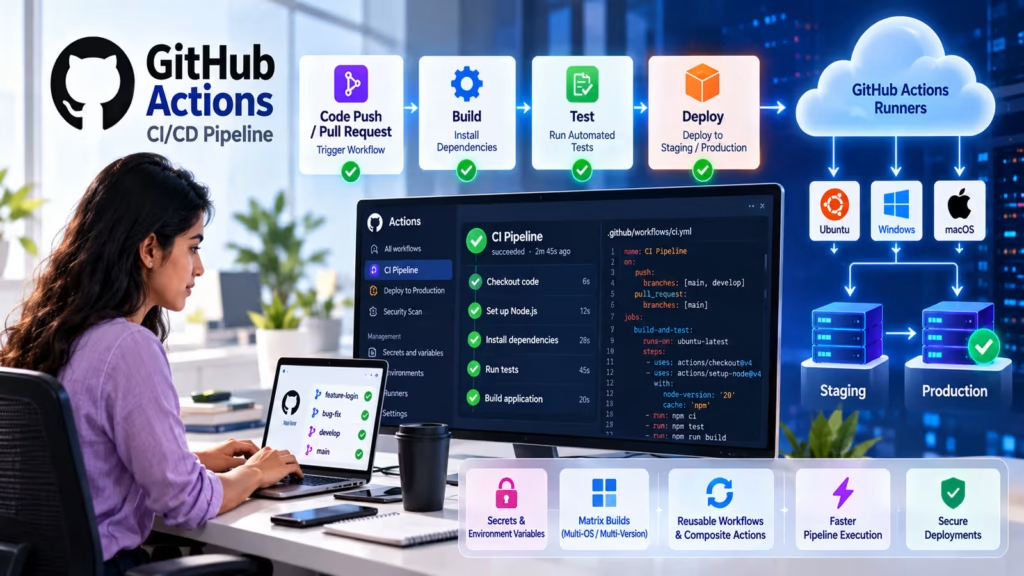
GitHub Actions automates workflows by responding to events that occur within a GitHub repository. When a developer pushes code, opens a pull request, merges a branch, creates a release tag, or even schedules a timed trigger, GitHub can automatically execute a defined workflow in response.
Each workflow is a YAML file stored in the .github/workflows/ directory of the repository. When the triggering event occurs, GitHub reads the relevant workflow file and executes it on a runner — a virtual machine that GitHub provisions automatically. Runners come in Ubuntu, Windows, and macOS variants. Ubuntu runners are the most commonly used due to their compatibility with most CI/CD tooling and their speed.
The core components of a GitHub Actions workflow are:
- Workflow — the overall automation defined in a YAML file
- Event — the trigger that starts the workflow (push, pull_request, schedule, workflow_dispatch, etc.)
- Job — a collection of steps that run on a single runner
- Step — an individual task within a job, either a shell command or an action
- Action — a reusable unit of functionality from the GitHub Actions marketplace or defined within the repository
Building a Basic CI Pipeline With GitHub Actions
A CI pipeline validates that code changes do not break existing functionality. The most basic version — checkout, install dependencies, run tests — can be expressed in fewer than 30 lines of YAML. Here is a complete example for a Node.js application:
name: CI Pipeline

on:
  push:
    branches: [main, develop]
  pull_request:
    branches: [main]

jobs:
  build-and-test:
    runs-on: ubuntu-latest
    steps:
      - name: Checkout code
        uses: actions/checkout@v4

      - name: Set up Node.js
        uses: actions/setup-node@v4
        with:
          node-version: '20'
          cache: 'npm'

      - name: Install dependencies
        run: npm ci

      - name: Run tests
        run: npm test

      - name: Build application
        run: npm run build
Save this file as .github/workflows/ci.yml and push it to your repository. From that point, every push to the main or develop branch, and every pull request targeting main, will automatically trigger this pipeline. Results appear directly in the GitHub interface — on the pull request, on the commit, and in the Actions tab of the repository.
Managing Secrets and Environment Variables
CI/CD pipelines routinely need access to sensitive values — API keys, deployment credentials, database connection strings, cloud provider tokens. Storing these directly in workflow files is never acceptable; they would be exposed in your repository history.
GitHub Actions provides encrypted secrets, stored at the repository or organization level, that are injected into workflow runs as environment variables. To add a secret, navigate to Settings > Secrets and variables > Actions in your repository, and add the key-value pair. In your workflow, reference it using the ${{ secrets.SECRET_NAME }} syntax:
- name: Deploy to AWS
  env:
    AWS_ACCESS_KEY_ID: ${{ secrets.AWS_ACCESS_KEY_ID }}
    AWS_SECRET_ACCESS_KEY: ${{ secrets.AWS_SECRET_ACCESS_KEY }}
  run: aws s3 sync ./build s3://my-bucket
For non-sensitive configuration that varies by environment — base URLs, feature flags, environment names — use environment variables defined at the job or step level. Secrets and variables are distinct: secrets are encrypted and masked in logs; variables are plain text and visible in workflow definitions.
Adding a CD Stage: Deploying to Production
A deployment job extends the CI pipeline by automatically pushing validated builds to a target environment. The deployment job should only run after the build-and-test job succeeds — this is enforced using the needs keyword:
  deploy:
    runs-on: ubuntu-latest
    needs: build-and-test
    if: github.ref == 'refs/heads/main'
    environment: production
    steps:
      - uses: actions/checkout@v4
      - name: Deploy to server
        run: |
          echo "Deploying build artifacts..."
          # Your deployment commands here
The if: github.ref == 'refs/heads/main' condition restricts deployment to the main branch only — pushes to feature branches run the CI job but skip deployment. The environment: production setting enables GitHub Environments, which adds optional protection rules such as required reviewers who must approve before the deployment proceeds.
Matrix Builds for Multi-Version Testing
The matrix strategy is one of the most powerful features in GitHub Actions. It allows a single job definition to run across multiple combinations of parameters — language versions, operating systems, database versions — simultaneously and independently.
jobs:
  test:
    runs-on: ${{ matrix.os }}
    strategy:
      matrix:
        os: [ubuntu-latest, windows-latest]
        node-version: [18, 20, 22]
    steps:
      - uses: actions/checkout@v4
      - uses: actions/setup-node@v4
        with:
          node-version: ${{ matrix.node-version }}
      - run: npm ci
      - run: npm test
This configuration generates six parallel jobs — every combination of two operating systems and three Node.js versions. Each job runs independently, and the overall workflow fails if any combination fails. Matrix builds catch compatibility issues that single-environment testing would miss, and they run in parallel so the total time is roughly the same as a single run.
Reusable Workflows and Composite Actions
As organizations grow their use of GitHub Actions, they often find that the same workflow patterns repeat across multiple repositories — the same build steps, the same deployment logic, the same security scanning jobs. Copy-pasting workflow YAML into every repository creates maintenance overhead: a change to the pattern requires updating every repository manually.
Reusable workflows solve this. A workflow can be marked as callable by other workflows using on: workflow_call, and other workflows in the same organization can reference it directly. When the reusable workflow is updated, all calling workflows automatically use the new version.
Composite actions go further by packaging multiple steps into a single named action that behaves like any other action in a workflow. These can be published to the GitHub Actions marketplace or kept private within an organization. For teams managing more than a handful of repositories, investing in reusable workflows and composite actions significantly reduces duplication and drift between pipeline configurations.
Caching Dependencies to Speed Up Pipelines
Installing dependencies on every workflow run adds significant time. An npm install that downloads hundreds of packages, or a Maven build that resolves dozens of dependencies, can consume several minutes per run that could be avoided entirely. GitHub Actions provides a built-in caching mechanism that stores dependency directories between runs and restores them when the cache key matches.
The actions/setup-node@v4, actions/setup-python@v5, and similar official setup actions accept a cache parameter that automatically handles caching for you. When the package-lock.json or requirements.txt file has not changed, the entire node_modules or .venv directory is restored from cache instead of being reinstalled. This alone can reduce pipeline execution time by two to five minutes per run, which compounds significantly over hundreds of daily runs across a development team.
Security Considerations for GitHub Actions Pipelines
Pipelines that deploy to production carry significant security responsibility. Several practices reduce risk in GitHub Actions workflows. Pin third-party actions to a specific commit SHA rather than a mutable tag — a tag like @v4 can be moved by the action’s author to point to different code, while a pinned SHA is immutable. Use the principle of least privilege for the GITHUB_TOKEN — grant only the permissions the workflow genuinely needs. Use GitHub Environments with required reviewers for production deployments to prevent unreviewed code from reaching production automatically. Enable Dependabot for Actions to receive automated pull requests when action dependencies have updates or known vulnerabilities.
Start Your Data Analytics Career Today
Join WhaleCourseTechnologies for affordable training with hands-on projects and placement support.
Conclusion
Building CI/CD pipelines using GitHub Actions is straightforward to start and scales well as your needs grow. The basic pattern — trigger on push, run on a hosted runner, execute build and test steps — gets most teams the majority of their value within an hour of setup. The more advanced features — matrix builds, reusable workflows, deployment environments, composite actions, and dependency caching — address the real-world complexity that appears as pipelines and repositories multiply.
The key to maintaining pipelines well is treating workflow YAML with the same discipline applied to application code. Review changes, version control secrets handling carefully, pin external dependencies, and invest in reusable patterns before duplication becomes a maintenance problem. GitHub Actions makes these practices achievable without deep DevOps infrastructure expertise, which is a genuine advantage for teams that want CI/CD automation without a dedicated platform engineering team.
In This Article
Enroll in Our IT Courses
Master IT Program at whalecoursetechnologies
- Expert Mentorship from IT Professionals
- Job-Ready Skills with Live Projects
- Career Boost Add-on Modules
- 100% Placement & Interview Support
